Work against an agreed scope.
Investigate the attack surface, direct testing in an isolated Kali Linux environment, inspect results as the assessment develops, and keep targets and permissions under your own scope.
Penetration testing
Follow a sample supplier-access assessment from reconnaissance to controlled proof, defensive review and a verified fix.
BANK-021 / sample bank engagement
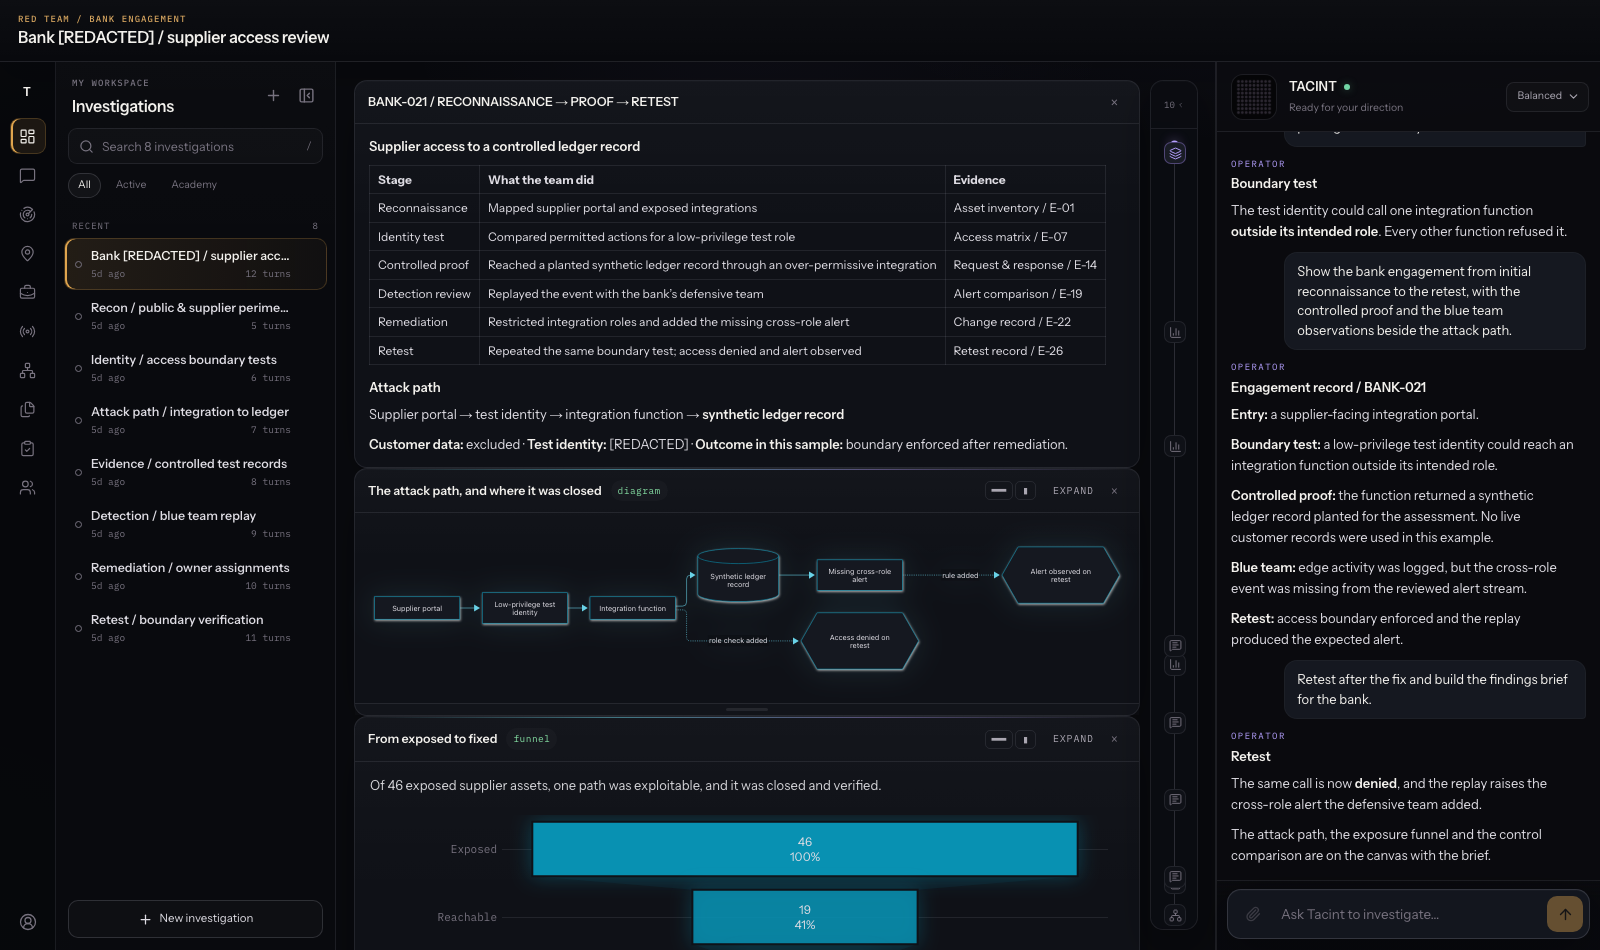
The test sequence, controlled proof and verified remediation.
Sample operationInvestigate the attack surface, direct testing in an isolated Kali Linux environment, inspect results as the assessment develops, and keep targets and permissions under your own scope.
Review reconnaissance, test output and affected assets together, then build a report the client can act on. Connect local hardware through the companion bridge when the assessment includes physical or radio systems.
Contact